

Can AI Crack Bitcoin? The Differences Between Cryptographic Attacks, Wallet Theft, and Quantum Computing
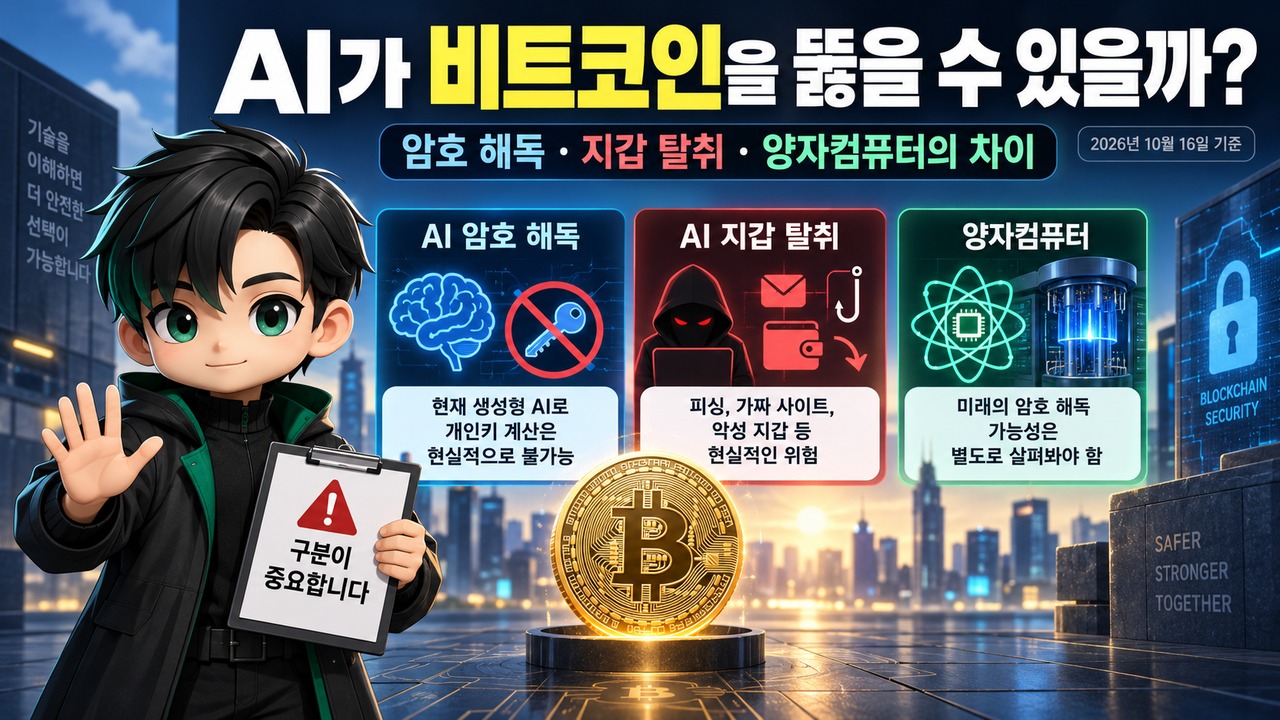
As of 2026-10-16, publicly available technical evidence does not support claims that ordinary generative AI can practically derive a properly generated Bitcoin private key. However, AI-assisted phishing and wallet theft are real risks, while the possibility of future quantum computers breaking cryptographic systems must be examined separately.
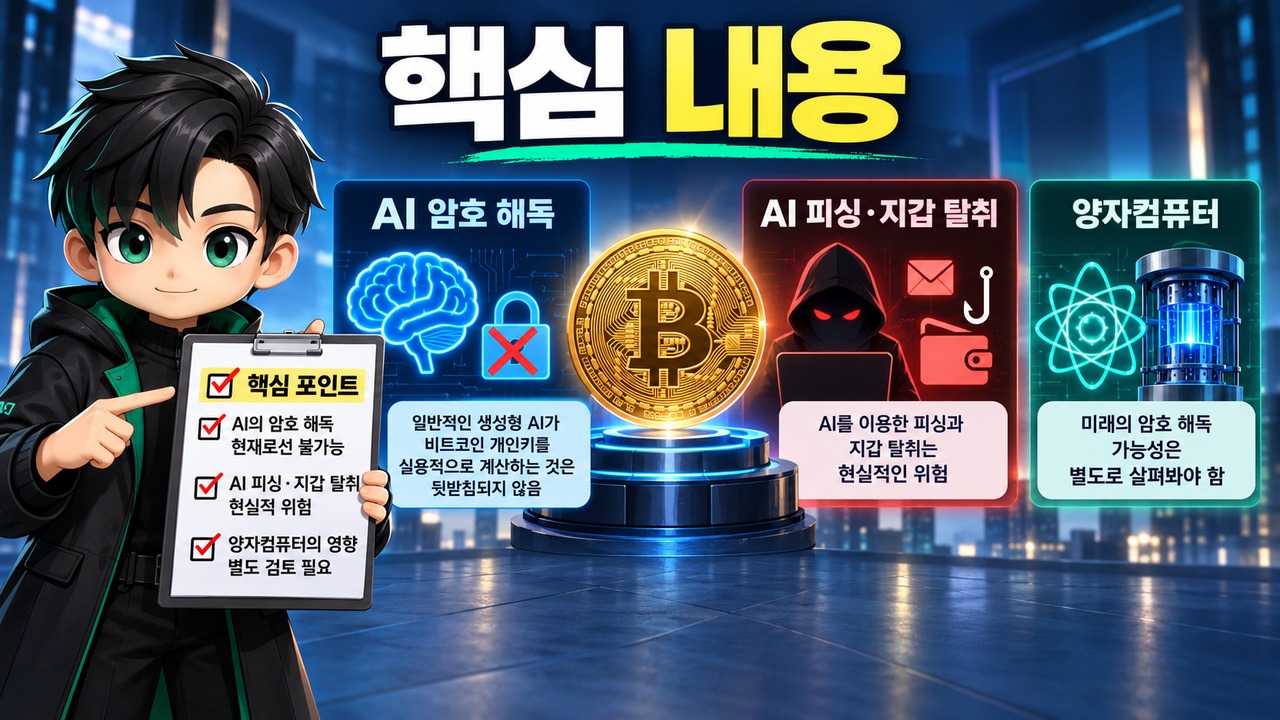
The key distinction is that breaking Bitcoin's cryptographic system and stealing someone's wallet are two entirely different problems.
Even if someone claims to have stolen Bitcoin using AI, the significance of the incident depends on whether they mathematically derived a private key, tricked a user into revealing a recovery phrase, or exploited vulnerable software.
So how does Bitcoin security actually work, and how much of a threat can AI realistically pose?
1. How Does Bitcoin Cryptography Work? The Roles of Private Keys, Digital Signatures, and SHA-256
Bitcoin is not a system protected by a single password. Digital signatures using private and public keys, hash functions that process transaction information, and network transaction validation rules all work together.
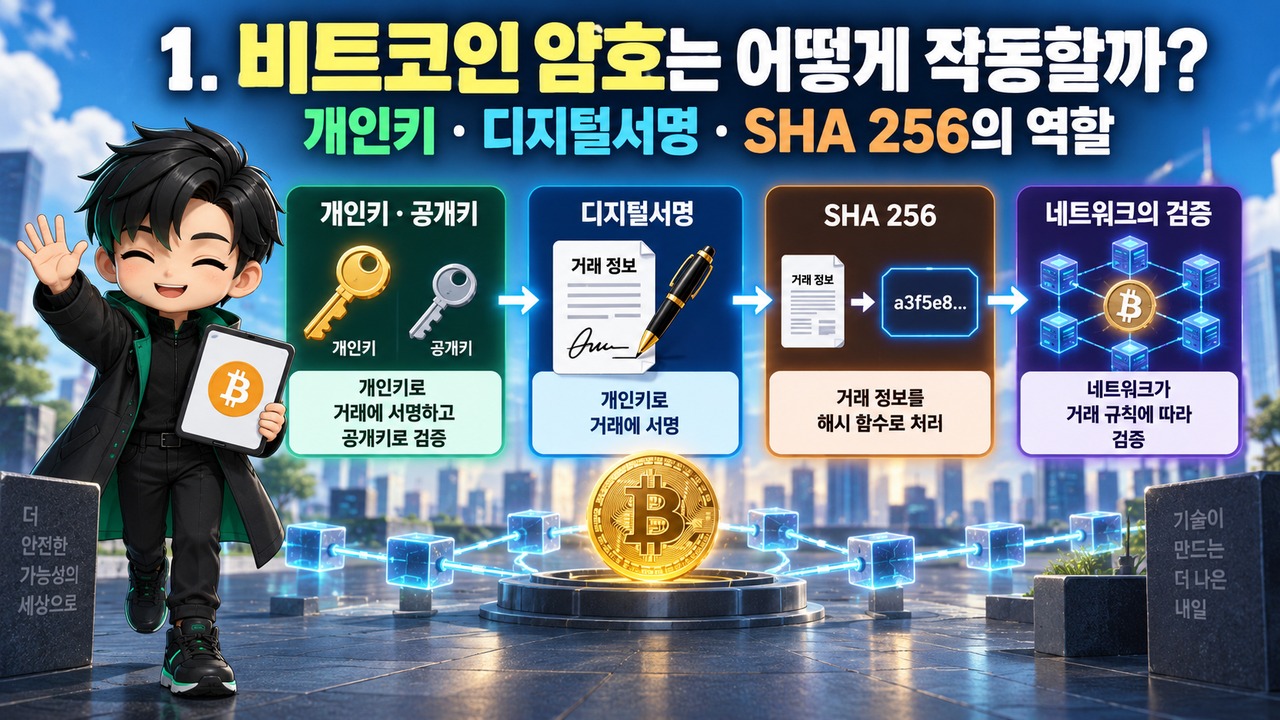
Each technology serves a different purpose. Therefore, a claim that AI can attack one component does not automatically mean Bitcoin's entire security system has been compromised.
First, a private key is secret information needed to prove authorization to spend Bitcoin.
A public key is mathematically related to its private key, but knowing a properly generated public key does not mean the corresponding private key can be easily determined.
When a Bitcoin wallet sends a transaction, it creates a digital signature using the private key. Network participants examine the public key, signature, and other information to verify that the transaction satisfies the established rules.
This process is explained in How Bitcoin Works on Bitcoin.org and the Bitcoin Developer Documentation.
There is an important technical distinction to understand here.
SHA-256 Is a Hash Function, While ECDSA and Schnorr Are Digital Signature Algorithms
SHA-256 is a function that converts input data into a fixed-length hash value. Bitcoin uses it in various processes, including block and transaction data processing and proof of work.
ECDSA, by contrast, is a digital signature scheme based on elliptic-curve cryptography. Bitcoin uses an elliptic curve called secp256k1, and ECDSA is used for signatures in traditional Bitcoin transactions.
Taproot also uses Schnorr signatures. Therefore, it would be inaccurate to describe all modern Bitcoin transaction signatures as relying exclusively on ECDSA.
The important distinction is as follows.
Attacking SHA-256 means challenging the security properties of a hash function, while attacking digital signatures involves mathematical problems related to signature forgery or private-key recovery.
The two are related, but they are not the same problem.
So could AI discover a private key simply by being given a publicly available Bitcoin wallet address?
Claims That AI Can Recover Private Keys From Properly Generated Bitcoin Addresses Alone Require Credible Verification
A Bitcoin address must also be distinguished from the public key itself. Depending on the address format, it may represent a hash of a public key or spending conditions, and the point at which a public key becomes visible during transactions can vary.
The ability to analyze a public address is entirely different from the ability to calculate the private key needed to spend the funds associated with that address.
2. What Are the Real Risks Behind Claims That AI Can Hack Bitcoin?
AI certainly has the potential to harm Bitcoin holders. However, the specific risks supported by currently available public evidence are more closely associated with impersonation, phishing, fraudulent services, and malicious software than with mathematically deriving cryptographic private keys.
Generative AI, in particular, can be misused to create deceptive messages and fabricated content.
The FBI's Internet Crime Complaint Center (IC3), in its warning about generative AI and financial fraud published December 2024, highlighted risks including AI-assisted impersonation and fraudulent cryptocurrency investment websites.
Criminals may use AI to write convincing customer-service messages or create content that appears to come from legitimate companies to gain users' trust.
If users visit fraudulent wallet websites or enter their recovery phrases during this process, they may lose their assets.
However, this does not prove that Bitcoin's digital signature algorithms have been mathematically broken.
The differences become clearer when the attack types are compared.
| Attack Type | Target | Meaning and Evaluation Criteria |
|---|---|---|
| Cryptographic private-key recovery | Mathematical relationship between public and private keys | Requires technical evidence demonstrating practical recovery of a securely generated key |
| AI phishing and impersonation | User judgment and authentication information | Losses can occur without breaking cryptography |
| Malicious wallets and seed phrase exposure | Wallet software and secret information | Exploits leaked information rather than mathematically deriving keys |
| Quantum computer attacks | Mathematical foundations of public-key cryptography | Long-term risk requiring sufficiently powerful quantum computers |
As the table shows, the fact that assets have been stolen does not, by itself, justify concluding that the underlying cryptographic system has been broken.
For example, a wallet's seed phrase is critical secret information used to restore multiple private keys. If the seed phrase is exposed, an attacker can access the wallet without solving a difficult mathematical problem.
Insecure wallet software and improperly implemented random-number generation methods also present separate risks.
The challenge of reverse-engineering a properly generated private key must be distinguished from the problem of using a private key that was predictable from the beginning.
The same distinction applies to AI's ability to help write or analyze program code. Strong coding capabilities do not mean that AI can generally solve mathematically difficult cryptographic problems designed to be computationally infeasible.
Therefore, if you encounter promotional claims such as 'AI can hack every Bitcoin wallet' or 'Enter an address to discover its private key,' you should first look for verifiable technical evidence.
Particular caution is needed with services that ask users to enter seed phrases under the pretext of verifying private keys or recovering wallets.
3. Can Quantum Computers Crack Bitcoin? A Long-Term Risk Different From AI
Quantum computers operate on fundamentally different principles from generative AI. While AI learns from data to generate text or code, quantum computers use quantum-mechanical properties to perform certain computations.
The crucial difference is that sufficiently powerful, fault-tolerant quantum computers could threaten some widely used public-key cryptographic systems.
In theory, Shor's algorithm can efficiently solve the mathematical problems underlying elliptic-curve cryptography on a suitable quantum computer.
Because Bitcoin's ECDSA and Schnorr signatures are also based on elliptic-curve cryptography, their long-term exposure to quantum computing risks must be examined.
However, a mathematically possible attack must be distinguished from one that can actually be executed in practice.
A real-world attack would require not only sufficient computational power but also technology capable of controlling errors and reliably performing the necessary operations.
The U.S. National Institute of Standards and Technology (NIST), in its explanation of post-quantum cryptography, describes the threats that future quantum computers could pose to existing public-key cryptography and emphasizes the need to develop cryptographic standards and prepare for their adoption.
However, exactly when sufficiently powerful quantum computers will become available remains uncertain.
Therefore, claims that Bitcoin cryptography will inevitably collapse in 2027 or any other particular year go beyond the publicly available evidence.
Quantum computers would not necessarily defeat every cryptographic technology in the same way.
Quantum attacks against public-key cryptography and quantum attacks against hash functions such as SHA-256 involve different algorithms and have different security implications.
The level of quantum attack exposure may also vary depending on whether a Bitcoin public key has been revealed and the conditions governing a transaction. Funds whose public keys have already been exposed should not be treated as having the same risk profile as funds whose public keys remain undisclosed.
Would switching Bitcoin to post-quantum cryptography solve the problem?
Researching technical countermeasures and actually introducing new signature rules into the Bitcoin network are separate processes.
Bitcoin is not a system in which a central administrator can unilaterally change transaction rules. Changing its cryptographic system would require technical review, software implementation, consideration of how existing funds would be migrated, and broad consensus and adoption among network participants.
The Bitcoin.org FAQ also discusses Bitcoin security issues and quantum computing threats as distinct concerns.
The fact that NIST has established post-quantum cryptographic standards does not mean those standards are automatically incorporated into the Bitcoin network.
Ultimately, the more useful question is not 'When will quantum computers destroy Bitcoin?' but rather 'Which cryptographic technologies could be affected, and what countermeasures could be adopted before a practical threat emerges?'
Security Checks Bitcoin Users Should Make Today
When evaluating Bitcoin security, users should consider both the possibility of cryptographic attacks in the distant future and the wallet theft risks that exist today.
The following basic precautions are important for ordinary users.
Obtain wallet software through official distribution channels and apply security updates.
Never share private keys or backup seed phrases with anyone, and avoid entering or exposing them online.
Independently verify messages claiming to come from customer support or requesting wallet connections through official channels.
Exercise caution if a wallet recovery company requests a seed phrase or guarantees successful recovery.
Avoid connecting wallets to suspicious websites or installing software from unknown sources.
If you suspect that your seed phrase has been exposed, consult the official security guidance for a trusted wallet and respond in a secure environment.
Bitcoin security depends not only on cryptographic algorithms but also on wallet software, private-key management, and user judgment.
The conclusion supported by publicly available evidence as of 2026-10-16 is clear.
Claims that ordinary generative AI can practically derive secure Bitcoin private keys have not been substantiated. However, AI-enabled wallet theft and financial fraud are real risks, and the long-term cryptographic threats posed by quantum computers require continued examination.
The current lack of evidence demonstrating successful private-key recovery should not be interpreted as proof that such an attack will remain impossible forever.
To understand Bitcoin security accurately, it is important to distinguish established technologies, real-world attack methods, and unresolved future risks rather than exaggerating AI's capabilities or assuming that cryptographic systems are absolutely secure.
※ This article is provided for informational purposes to help readers understand market developments and does not constitute an investment recommendation for any particular security or asset. All final investment decisions and associated responsibilities rest with the individual investor.
Related Articles
Drawing Trendlines on Bitcoin Charts for Beginners: How to Connect 2 Lows and 2 Highs